
The following sections list every released version of IAM, newest first. Each section comes from the monthly OCP® Release Notes page named in its Released line.
IAM 3.13.0
Released: October 2026
|
US1 |
US2 |
EU1 |
|---|---|---|
|
— |
— |
— |
Improvements
-
Faster Organization Selection in OCP Console® — Loading the organization list in OCP Console® is now faster, reducing wait time when switching between organizations.
-
PAT expiration emails now include the environment URL
IAM 3.12.1
Released: October 2026
|
US1 |
US2 |
EU1 |
|---|---|---|
|
— |
— |
— |
-
This release includes security updates.
IAM 3.12.0
Released: July 2026
|
US1 |
US2 |
EU1 |
|---|---|---|
|
August 17, 2026 |
Rolled-forward |
August 17, 2026 |
Improvements
-
Expanded Organization Admin Capacity - Organizations can now assign administrator access to twice as many users as before, giving larger support teams the access they need to help end customers without hitting a limit.
-
Smoother Group Role Updates - Updating role assignments for groups now works reliably even in organizations with many custom roles, removing a barrier for admins managing complex permission setups.
Fixes
-
Prevented Duplicate and System Role Names - Custom role creation now blocks names that match existing system roles or other custom roles, preventing the confusion and access issues that duplicate names used to cause.
IAM 3.11.0
Released: June 2026
|
US1 |
US2 |
EU1 |
|---|---|---|
|
Rolled-forward |
Rolled-forward |
Rolled-forward |
New Features
-
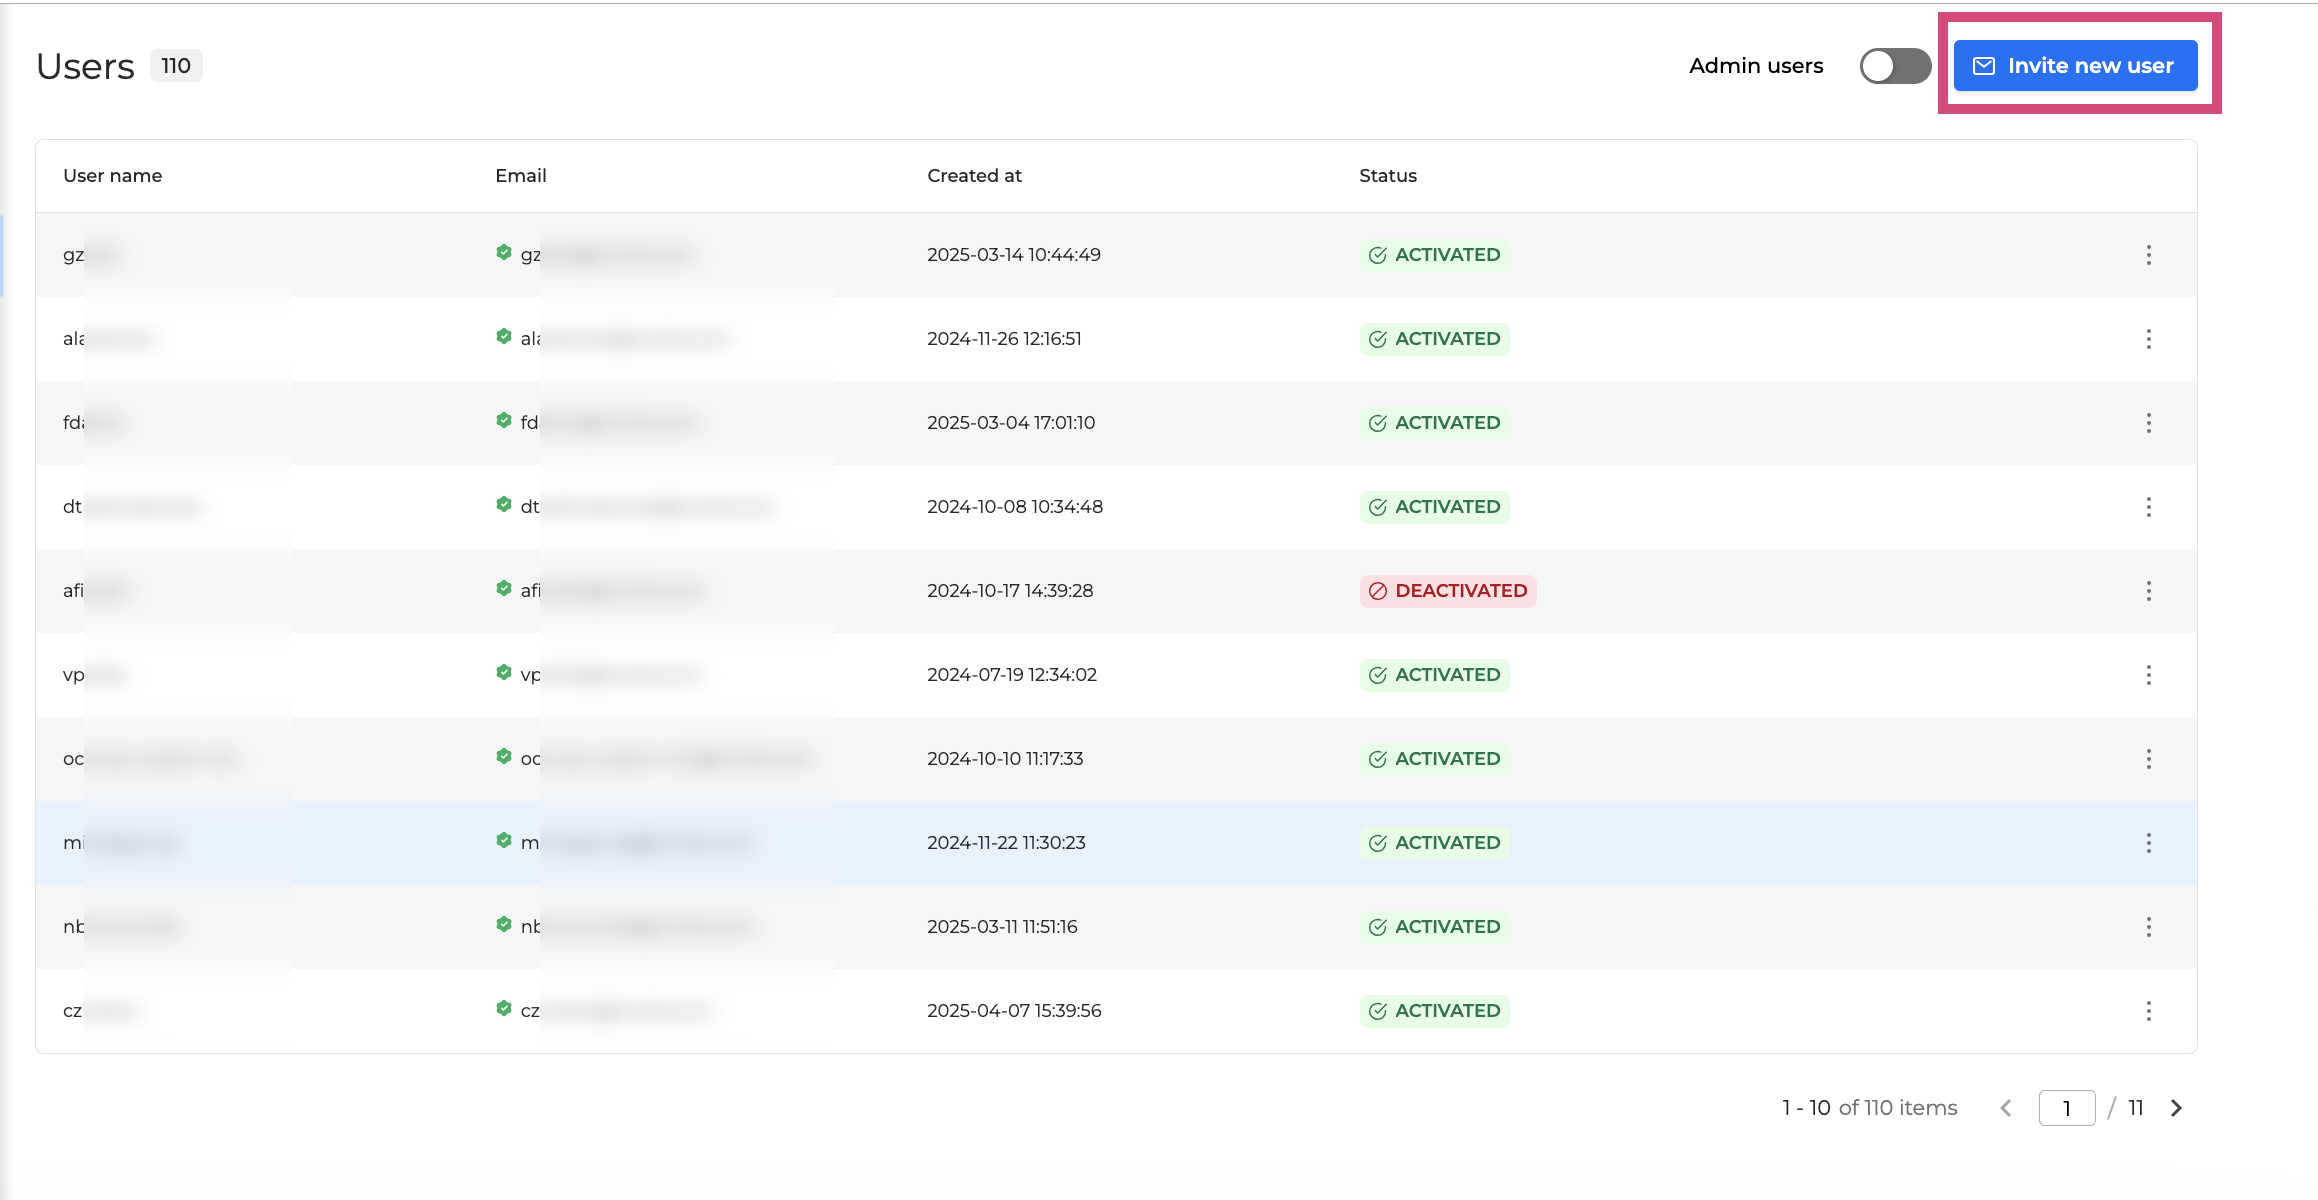
Invite New Users by Email - Organization admins can now invite new users directly by email from OCP Console. The invited user receives a time-limited link to set their own password and is logged in immediately after. Public self-registration can be disabled as a result, giving administrators tighter control over who joins their organization.
-
Admin-Initiated Password Reset - OCP Console and organization admins can now reset a user's password directly from the user list or the user's details view. This removes the need for a public "Forgot Password" link, reducing the attack surface for credential abuse while letting admins resolve access issues without involving support.
Improvements
-
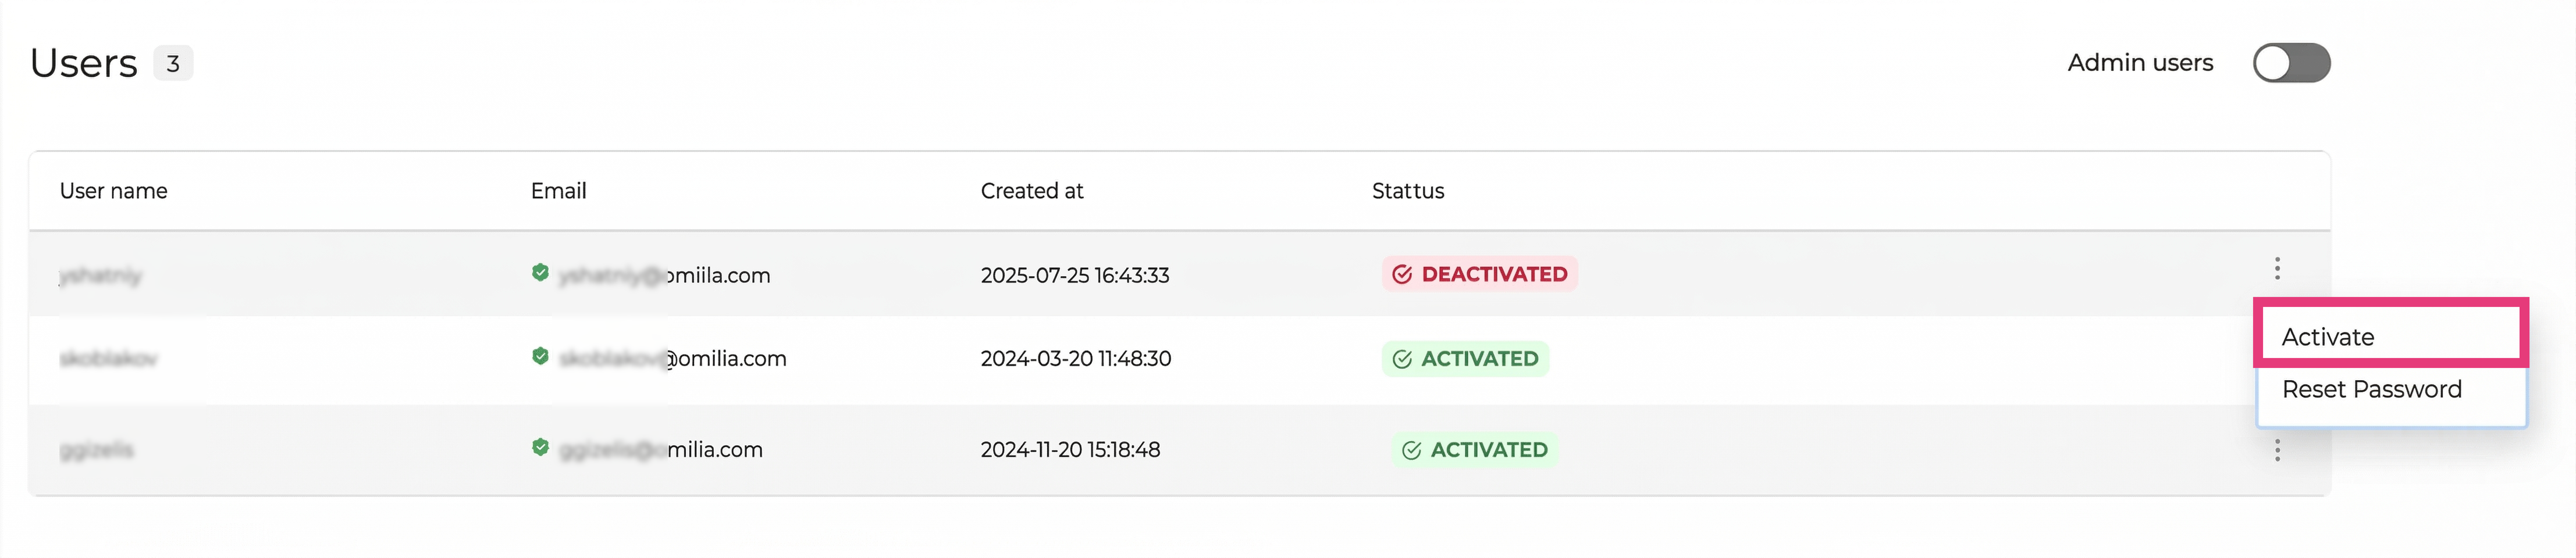
User Reactivation by Organization Admins - Organization admins can now reactivate a deactivated user in their organization without raising a support request. This applies even when the user belongs to multiple organizations, and all reactivation actions are logged for audit purposes.
-
Cleaner Email Sender Display - System emails such as password change notifications and inactivity alerts now display a clean, domain-appropriate sender name instead of a raw technical address. On white-label environments, Omilia branding is not shown in the sender field.
-
Earlier Notification Before Personal Access Token Expiry - Users now receive an additional reminder 30 days before their personal access token expires, giving more time to renew tokens before access is interrupted.
-
Automatic Disablement of Inactive Service Accounts - Service accounts that have been inactive for 90 days are now disabled automatically, with an advance alert sent at 60 days. This keeps the platform in line with access-control best practices and reduces the risk from dormant credentials.
-
Refreshed OCP Console Interface - Phase 1 - The OCP® Console user interface has been updated as part of a wider overhaul initiative, delivering a more consistent and refined experience.
Fixes
-
Corrected Wording in System Email Notifications - Grammar errors in account lock and token expiry notification emails have been corrected, ensuring all automated messages read clearly and professionally.
-
This release includes security updates.
For more information go to Access Management Tab.
IAM 3.10.0
Released: February 2026
|
US1 |
US2 |
EU1 |
|---|---|---|
|
May 12, 2026 |
May 18, 2026 |
May 19, 2026 |
Added
-
IAM keyboard navigation support
-
Trial attribute on users is interactive
-
Audit logs admin view
-
Improved logging information clarity
-
Ability to Create, Edit Organisation's policy
-
Automated email warns of PAT expiration
Changed
-
Improved "account is disabled" message
-
Inactivity userlock email set to 14, 7, 2 days before deactivation
-
omAccounts version updated
-
PATs have mandatory expiration under 365 days
IAM 3.9.2
Released: February 2026
|
US1 |
US2 |
EU1 |
|---|---|---|
|
February 16, 2026 |
Rolled-forward |
February 24, 2026 |
-
Logging improvement
-
Backwards compatibility addition
-
omAccounts updated to 26.5.2.1
-
Security updates
IAM v3.9.0
Released: November 2025
|
US1 |
US2 |
EU1 |
|---|---|---|
|
Rolled-forward |
Rolled-forward |
Rolled-forward |
Added
-
Interface for administrators to view priority log events
-
Ability for users to view Organisation’s administrators and users
Fixed
-
Security updates
IAM v3.8.0
Released: July 2025
|
US1 |
US2 |
EU1 |
|---|---|---|
|
August 18, 2025 |
August 25, 2025 |
August 19, 2025 |
Added
-
Additional support for service accounts in admin IAM
-
View option for admin IAM policies
-
Support for automated creation of permission and policies on rollout
-
Deactivation of inactive accounts
Changed
-
Side menus, tab names truncated
Fixed
-
Number of security updates
IAM v3.7.1
Released: June 2025
|
US1 |
US2 |
EU1 |
|---|---|---|
|
July 9, 2025 |
July 15, 2025 |
June 30, 2025 |
This release includes small bug fixes
IAM v3.7.0
Released: May 2025
|
US1 |
US2 |
EU1 |
|---|---|---|
|
June 12, 2025 |
June 17, 2025 |
June 30, 2025 |
Added
-
Additional validation on group names when creating a group
-
WFAI Service
-
Audio-hup-api Service
-
Alerts Service
-
Minor UI updates
-
Adjustable UI elements for exclusive environments
Changed
-
Max session limiter counts SA and browser sessions limits separately
-
Improved custom browser login flow handling
-
Validation on group names improves
Removed
-
Allow import from user's details tab
Fixed
-
Dropdown menus the next offset page bug
-
Public IAM users page not changed for admins
-
Public IAM page limits Org admins list
-
Security updates
IAM v3.6.2
Released: April 2025
|
US1 |
US2 |
EU1 |
|---|---|---|
|
Rolled-forward |
Rolled-forward |
Rolled-forward |
Fixed
-
Security update for the following components:
-
iam-api -
idm-api -
idm-energon -
omaccounts -
iam-sidecar
-
IAM v3.6.0
Released: March 2025
|
US1 |
US2 |
EU1 |
|---|---|---|
|
Rolled-forward |
Rolled-forward |
Rolled-forward |
Added
-
Explicit logging event for user deactivation on admin backend
-
Admin endpoint for prolonged exchange token duration
-
Search for permissions list in admin interface
-
Capability for services to set up initial permissions, policies automatically
Changed
-
Prompt to add users to the group change to highlight full email is needed
-
Billing context includes IAM context
-
Password expiration and lengths across number of environments
-
Organisation selector sort minds lower and upper case
-
IAM browser's tab name improved for uniformity
Removed
-
PAT exchange for deactivated users
For more information, go to OCP Console® User Guide.
IAM v3.5.1
Released: February 2025
|
US1 |
US2 |
EU1 |
|---|---|---|
|
Rolled-forward |
Rolled-forward |
Rolled-forward |
Added
-
Additional validation on duplicate name while creating new Group
-
Error “user in a group” features username
-
Role can be added in User's details
-
Public group list has search functionality
Changed
-
Sort and search in public user's list is improved
-
Permissions, policies views of public Access Management are hidden
-
Group creation in internal IAM has Organisation as mandatory field
Fixed
-
Bug with saving policies without roles
-
Regular security updates
For more information, go to OCP Console® User Guide.
IAM v3.4.0
Released: December 2024
|
US1 |
US2 |
EU1 |
|---|---|---|
|
Rolled-forward |
Rolled-forward |
Rolled-forward |
Added
-
German language support for OCP interface in selected environments
-
Edit and revoke User’s Service Roles functions in administrative interface
-
Organization’s administrators can toggle for Users list to show Organisations administrators
-
Ability for services to check if user is an Organisation’s administrator
-
Authorization on multiple groups
-
Security update
Changed
-
Session limiting coverage for custom login flow
Fixed
-
Customer roles feature flag doesn't affect admin interface
-
List Organisations endpoint pagination bug
IAM v3.3.0
Released:
|
US1 |
US2 |
EU1 |
|---|---|---|
|
Rolled-forward |
Rolled-forward |
Rolled-forward |
Added
-
Monitoring service
-
Capability for the support of multiple languages
-
Security updates
Changed
-
Increased limits on concurrent sessions of a user
-
Fixed error handling on some cases
Removed
-
Unsupported ciphers
IAM v3.2.0
Released:
|
US1 |
US2 |
EU1 |
|---|---|---|
|
Rolled-forward |
Rolled-forward |
Rolled-forward |
Added
-
Number of new service accounts for components
-
Security updates and fixes
-
Allow importattribute in Attributes section of the administrative IAM interface applicable
IAM v3.1.0
Released:
|
US1 |
US2 |
EU1 |
|---|---|---|
|
Rolled-forward |
Rolled-forward |
Rolled-forward |
Added
-
User deactivation context for the Access Management UI, API
-
Pagination to IAM public Organisation's Groups view
-
Support for multiple Administrators in an Organisation
-
Options for services in Policies
-
Navigation to the User's view from Organisation’s Groups view
-
Organisation’s User’s Details updated with broader information
Changed
-
Date format in IAM UI is changed to ISO: YYYY:MM:DD HH:MM:SS
-
Limit on service accounts in Policies UI increased
Fixed
-
Organisation’s administrators duplication in the Group members list
-
User’s Policies list filtration